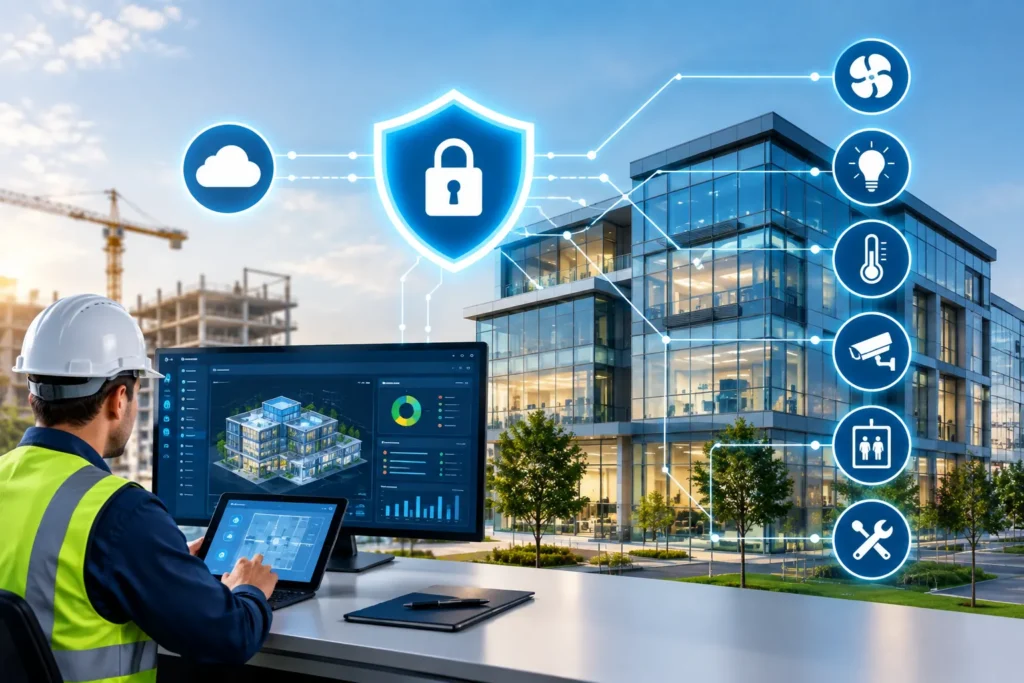
- Interconnected Operational Technology (OT) are used in modern commercial facilities and smart infrastructure to:
- regulate HVAC climate loops,
- automate lighting schedules,
- optimize energy consumption,
- manage physical access control systems.
However, physical facilities face elevated digital exposure, because Information Technology (IT) networks converge with building control hardware. Forming robust building management system for cyber security is a critical engineering obligation for operational continuity, life safety, and enterprise risk management instead of an optional facility improvement.
IBM Cost of a Data Breach Report states that the international average cost of an industrial data breach reached $4.88 million. Data breach incidents are even higher in critical infrastructure and industrial because of prolonged operational downtime. In smart facility environments, compromised control loops can lead to:
- physical equipment destruction,
- tenant lockouts,
- environmental falsification.
As real estate developers combine cloud-connected IoT sensors, instituting defensive controls across every field controller becomes critical for protecting building assets.
What is a Building Maintenance System BMS? Technical Fundamentals
A building maintenance system (BMS) is normally known as a BMS building maintenance system or Building Automation System (BAS). It is a computerized control framework that is installed across commercial real estate to monitor and implement mechanical, electrical, and electromechanical operations.
Multi-Tiered Control Architecture
How you can secure a facility; it requires analyzing the three operational tiers of a building maintenance system BMS:
- Field Level: Microprocessors, physical sensors, variable rate drives (VFDs), and actuators joined to mechanical assets such as chillers, boilers, and air handling units (AHUs).
- Automation Level: Field controllers processing operative logic through industrial communication protocols, comprising legacy BACnet (Building Automation and Control networks), Modbus TCP, and Lon Works.
- Management Level: Centrally supervisory workstations, human-machine interfaces (HMIs), and cloud management portals where facility engineers amend functioning setpoints, trends, and alarm thresholds.
Over all, these protocols ran over physically separated serial connections (RS-485) without encryption or password authentication. Today, for making dedicated building management system cyber security vital, IP-connected field devices expose unencrypted communication loops directly to internal enterprise LANs and public internet gateways.
Modern Security Threats & Risks in Smart Construction
Linking legacy operational hardware to enterprise cloud networks establishes multi-vector attack paths across commercial properties, healthcare centers, and industrial facilities.
Basic Attack Vectors in Smart Facilities
- Sideways Movement to Enterprise IT: Threat players that compromise edge devices (like IP-enabled thermostats) to pivot laterally into corporate networks, exfiltrating customer PII or proprietary business data.
- Unauthenticated Protocol Running: Cleartext protocols like BACnet/IP permit unauthorized actors for injecting fabricated command packets, changing temperature setpoints or inducing fire dampers open.
- Ransomware & Operational Halt: Adversaries secure supervisory HMIs, switching off environmental cooling in data centers or hospital operating rooms until ransom demands are satisfied.
- Unmonitored Supply Chain Backdoors: Third-party HVAC and mechanical contractors using unencrypted remote desktop connections found unmonitored entries into the facility network.
Everyday headlines in building automation cybersecurity news today and major BMS cybersecurity news bulletins emphasize that threat actors actively scanning Shodan engines for unpatched building controllers exposed directly to public IP addresses.
Best Practices for Executing Building Automation Cyber Security
Securing a BMS building maintenance system commands applying defense-in-depth architecture that relates hardware hardening, network micro-segmentation, and strict access governance.
Step-by-Step System Hardening Strategy
- Network Micro-Segmentation: Separate the BMS building maintenance system onto dedicated Virtual Local Area Networks (VLANs) controlled by industrial firewalls utilizing deep packet inspection (DPI).
- Migrate to BACnet/SC (Secure Connect): Substitute defenseless BACnet/IP connections with BACnet/SC, encapsulating operational traffic within encrypted TLS 1.3 WebSocket safeguarded by digital certificates.
- Enforce Zero Trust Remote Access: Employ Firm Identity and Access Management (IAM), steering Multi-Factor Authentication (MFA) and Least-Privilege Role-Based Access Control (RBAC) for all third-party maintenance sessions.
- Position Continuous Passive OT Monitoring: Place intrusion revealing sensors at network aggregation points to spot anomalous firmware updates, unauthorized IP additions, or unusual control commands.
- Establish Structured Patch Management: Uphold an active asset inventory of field controller firmware versions and conduct planned security patch validation before deployment.
The Role of a Specialized Building System Cybersecurity Firm
Managing operational technology security involves specialized engineering skill sets that traditional corporate IT teams seldom possess. Engaging an expert building system cybersecurity firm guarantees that security policies are aligned with physical engineering constraints without taking risk of unplanned operational downtime.
A competent building system cybersecurity firm provides critical technical services:
- OT-Specific Penetration Testing: Modelling targeted incidents against supervisory HMIs, wireless sensor networks, and field controllers without disturbing live building functions.
- Regulatory & Framework Compliance: Mapping building control architectures against international standards such as IEC 62443 and NIST SP 800-82 Rev. 3.
- Threat Modeling & Vulnerability Assessments: Organizing high-risk digital assets across composite commercial, housing, and industrial properties.
- Vendor Access Architecture Design: Developing secure zero-trust outside access pathways for external mechanical and electrical contractors.
Fiscal Analysis: Costs, ROI, and Budgeting for BMS Cybersecurity
Allocating capital for operational security involves detailed financial evaluation, comparing expenses of implementation against potential breach losses.
Breakdown of BMS Cybersecurity Implementation Cost
The direct BMS cybersecurity implementation cost changes, It depends on square footage, controller count, and legacy network infrastructure as shown in the table below:
| Implementation Phase | Description | Estimated Financial Investment |
|---|---|---|
| OT Security Audits & Asset Discovery | Baseline architecture reviews, vulnerability scans, and threat reviews | $15,000 – $45,000 |
| Industrial Firewalls & Hardware Modules | Next-generation OT firewalls, hardware security modules, and security gateways | $10,000 – $35,000 |
| Software Licensing (Monitoring & IAM) | Network abnormality monitoring software and zero-trust remote access licensing | $8,000 – $25,000 / year |
| Managed OT SOC Oversight | Managed threat recognition and 24/7 security operations center monitoring | $2,000 – $6,000 / month |
In new construction projects, combining building automation cyber security during initial design accounts for 1% to 2.5% of total MEP (Mechanical, Electrical, Plumbing) contract values. On the contrary, retrofitting legacy facilities can cost up to 3 times more due to hardware replacements.
Financial ROI & Cost-Benefit Analysis
The financial return on investment (ROI) is calculated using the Annualized Loss Expectancy (ALE) model:
ALE=Single Loss Expectancy (SLE)Annualized Rate of Occurrence (ARO)
If an unmitigated OT breach results in $800,000 in physical remediation, operational interruption, and forensic costs (SLE) with a 25% guessed annual likelihood (ARO = 0.25), the annual risk exposure becomes equal to $200,000. Allocating a $50,000 annual BMS cybersecurity implementation cost to remove that vulnerability yields an effective 300% annual return in avoided loss.
Additionally, deploying established building management system cyber security controls often decreases commercial property and cyber insurance premiums significantly.
Pros & Cons of Connected vs. Air-Gapped BMS Environments
| Pros | Cons | |
| Fully Connected Smart BMS | Continuous energy optimization centralized multi-site management, automated fault detection, predictive maintenance analytics | Larger digital attack surface, exposure to remote exploit chains, mandatory ongoing encryption management |
| Air-Gapped / Isolated BMS | Complete isolation from internet-borne attack vectors, simple initial regulatory isolation. | High manual maintenance overhead, inability to control real-time vendor cloud updates, risk of unmonitored USB filling gaps during physical service calls. |
Real-World Applications & Industry Use Cases
Designing building automation cyber security approaches depends heavily on facility use cases:
- Commercial Office Buildings: Multi-tenant towers manipulate VLAN micro-segmentation for separating tenant enterprise networks from central chiller plants and elevator control loops.
- Healthcare Facilities: Hospitals impose zero-trust guidelines to safeguard operating room air pressure controls and pharmaceutical refrigeration systems from external interfering.
- Data Centers: Mission-critical facilities join physical access locks with air-gapped monitoring networks to safeguard power distribution units (PDUs) and computer room air handlers (CRAHs).
Conclusion & Next Steps
Securing a modern building maintenance system BMS is a critical operational obligation for contemporary real estate engineering. Facility operators can protect physical assets, safeguard business continuity, and maximize operational ROI by substituting vulnerable legacy cleartext protocols, implementing zero-trust access controls, and partnering with a skilled building system cybersecurity firm,.
Ready to secure your smart building infrastructure? Contact our operational technology security engineers today to schedule a comprehensive OT cyber risk audit for your facility.